HIPAA-aware is an architecture. HIPAA-compliant is a posture you hold.
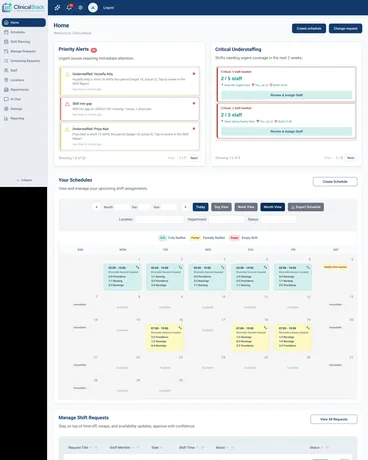
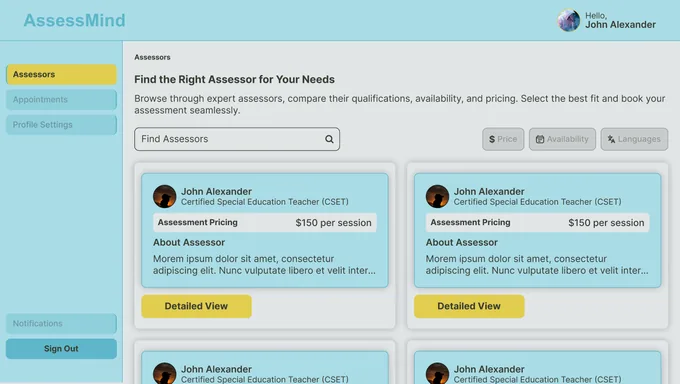
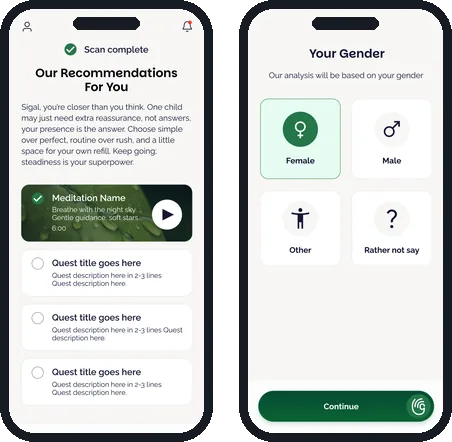
The software side of HIPAA is a short list that most builds still get wrong: PHI only ever touches vendors that will sign a BAA, every role sees exactly the data its job needs, every record access lands in an audit log, data is encrypted in transit and at rest, and there are working export and delete flows before launch rather than a promise of them. That is what we mean by HIPAA-aware, and it is in the first wireframe, not a hardening sprint at the end.
Keep reading
Compliance itself is organisational: policies, training, agreements, breach procedures. That lives with you as the covered entity or business associate. Our job is to make sure the software is never the weak link, and to be direct about where you need counsel.
 RaftWorks